How it works
A reasoning model built for one job: finding what's exploitable
EdgeBreach runs on our own reasoning model, trained specifically for software vulnerabilities. Here's how it tests your applications, what it proves, and how it does that without breaking anything.
The engine
Not a general-purpose AI with security prompts
Most "AI security" tools put a general-purpose model in front of existing scanners. The model issues a command, the tool returns a wall of text, and the model tries to parse meaning back out of it. Each step starts from scratch, and the result is only as good as the tools being wrapped.
EdgeBreach works the other way around. Our reasoning model, which we trained and run on our own infrastructure, sits at the center of the system. It receives structured data, decides what to try, acts through a small set of purpose-built tools, observes the result, and adapts, all within one continuous session. That's what we mean by AI-native: the model is the engine, not an add-on.
AI WRAPPER
EDGEBREACH
- 100%
- SCORE ON THE XBOW PENETRATION TESTING BENCHMARK
- 50+
- TRAINING ITERATIONS OF OUR OWN MODEL
- Under 5%
- FALSE-POSITIVE RATE ON PROVEN FINDINGS, INTERNAL MEASUREMENT
The platform behind the results
Three stages that prove what actually matters
01
Map your attack surface before attackers do
EdgeBreach maps every exposed service, port, and potential entry point, and shows you what changed since the last scan.
What happens:
- Port scanning and service detection
- Technology fingerprinting (frameworks, versions, configurations)
- API endpoint discovery
- DNS enumeration and subdomain mapping
- Cloud asset identification
Our fingerprinting uses multi-signal correlation, not just banner grabbing. We combine HTTP headers, error messages, cookies, and path patterns to build accurate technology profiles.
02
AI reasoning that learns your defenses
Our reasoning model analyzes your environment and plans attacks for your technology stack, your configurations, and your defenses.
What happens:
- Custom attack vector generation based on discovered technologies
- Business logic analysis (not just pattern matching)
- WAF detection and bypass selection
- Attack chain hypothesis formation
- Real-time adaptation based on responses
Traditional scanners ask: "Is this version in the CVE database?" EdgeBreach asks: "Given this Express API behind nginx with JWT auth, what attack chains should we explore?"
03
Exploitation that shows what actually matters
EdgeBreach doesn't just report theoretical vulnerabilities. We chain findings into real attack paths, execute them, and capture evidence proving exactly what an attacker could do.
What happens:
- Vulnerability exploitation with evidence capture
- Attack chain execution (LOW + MEDIUM = CRITICAL)
- Screenshot and HTTP request/response capture
- Redacted data samples where exposure has to be shown
- Remediation validation on demand
Every proven finding includes the proof. Not "possible SQL injection," but "SQL injection exploited: here's the request that worked, what it returned, and how to fix it." Findings it can't fully prove are reported with a confidence level.
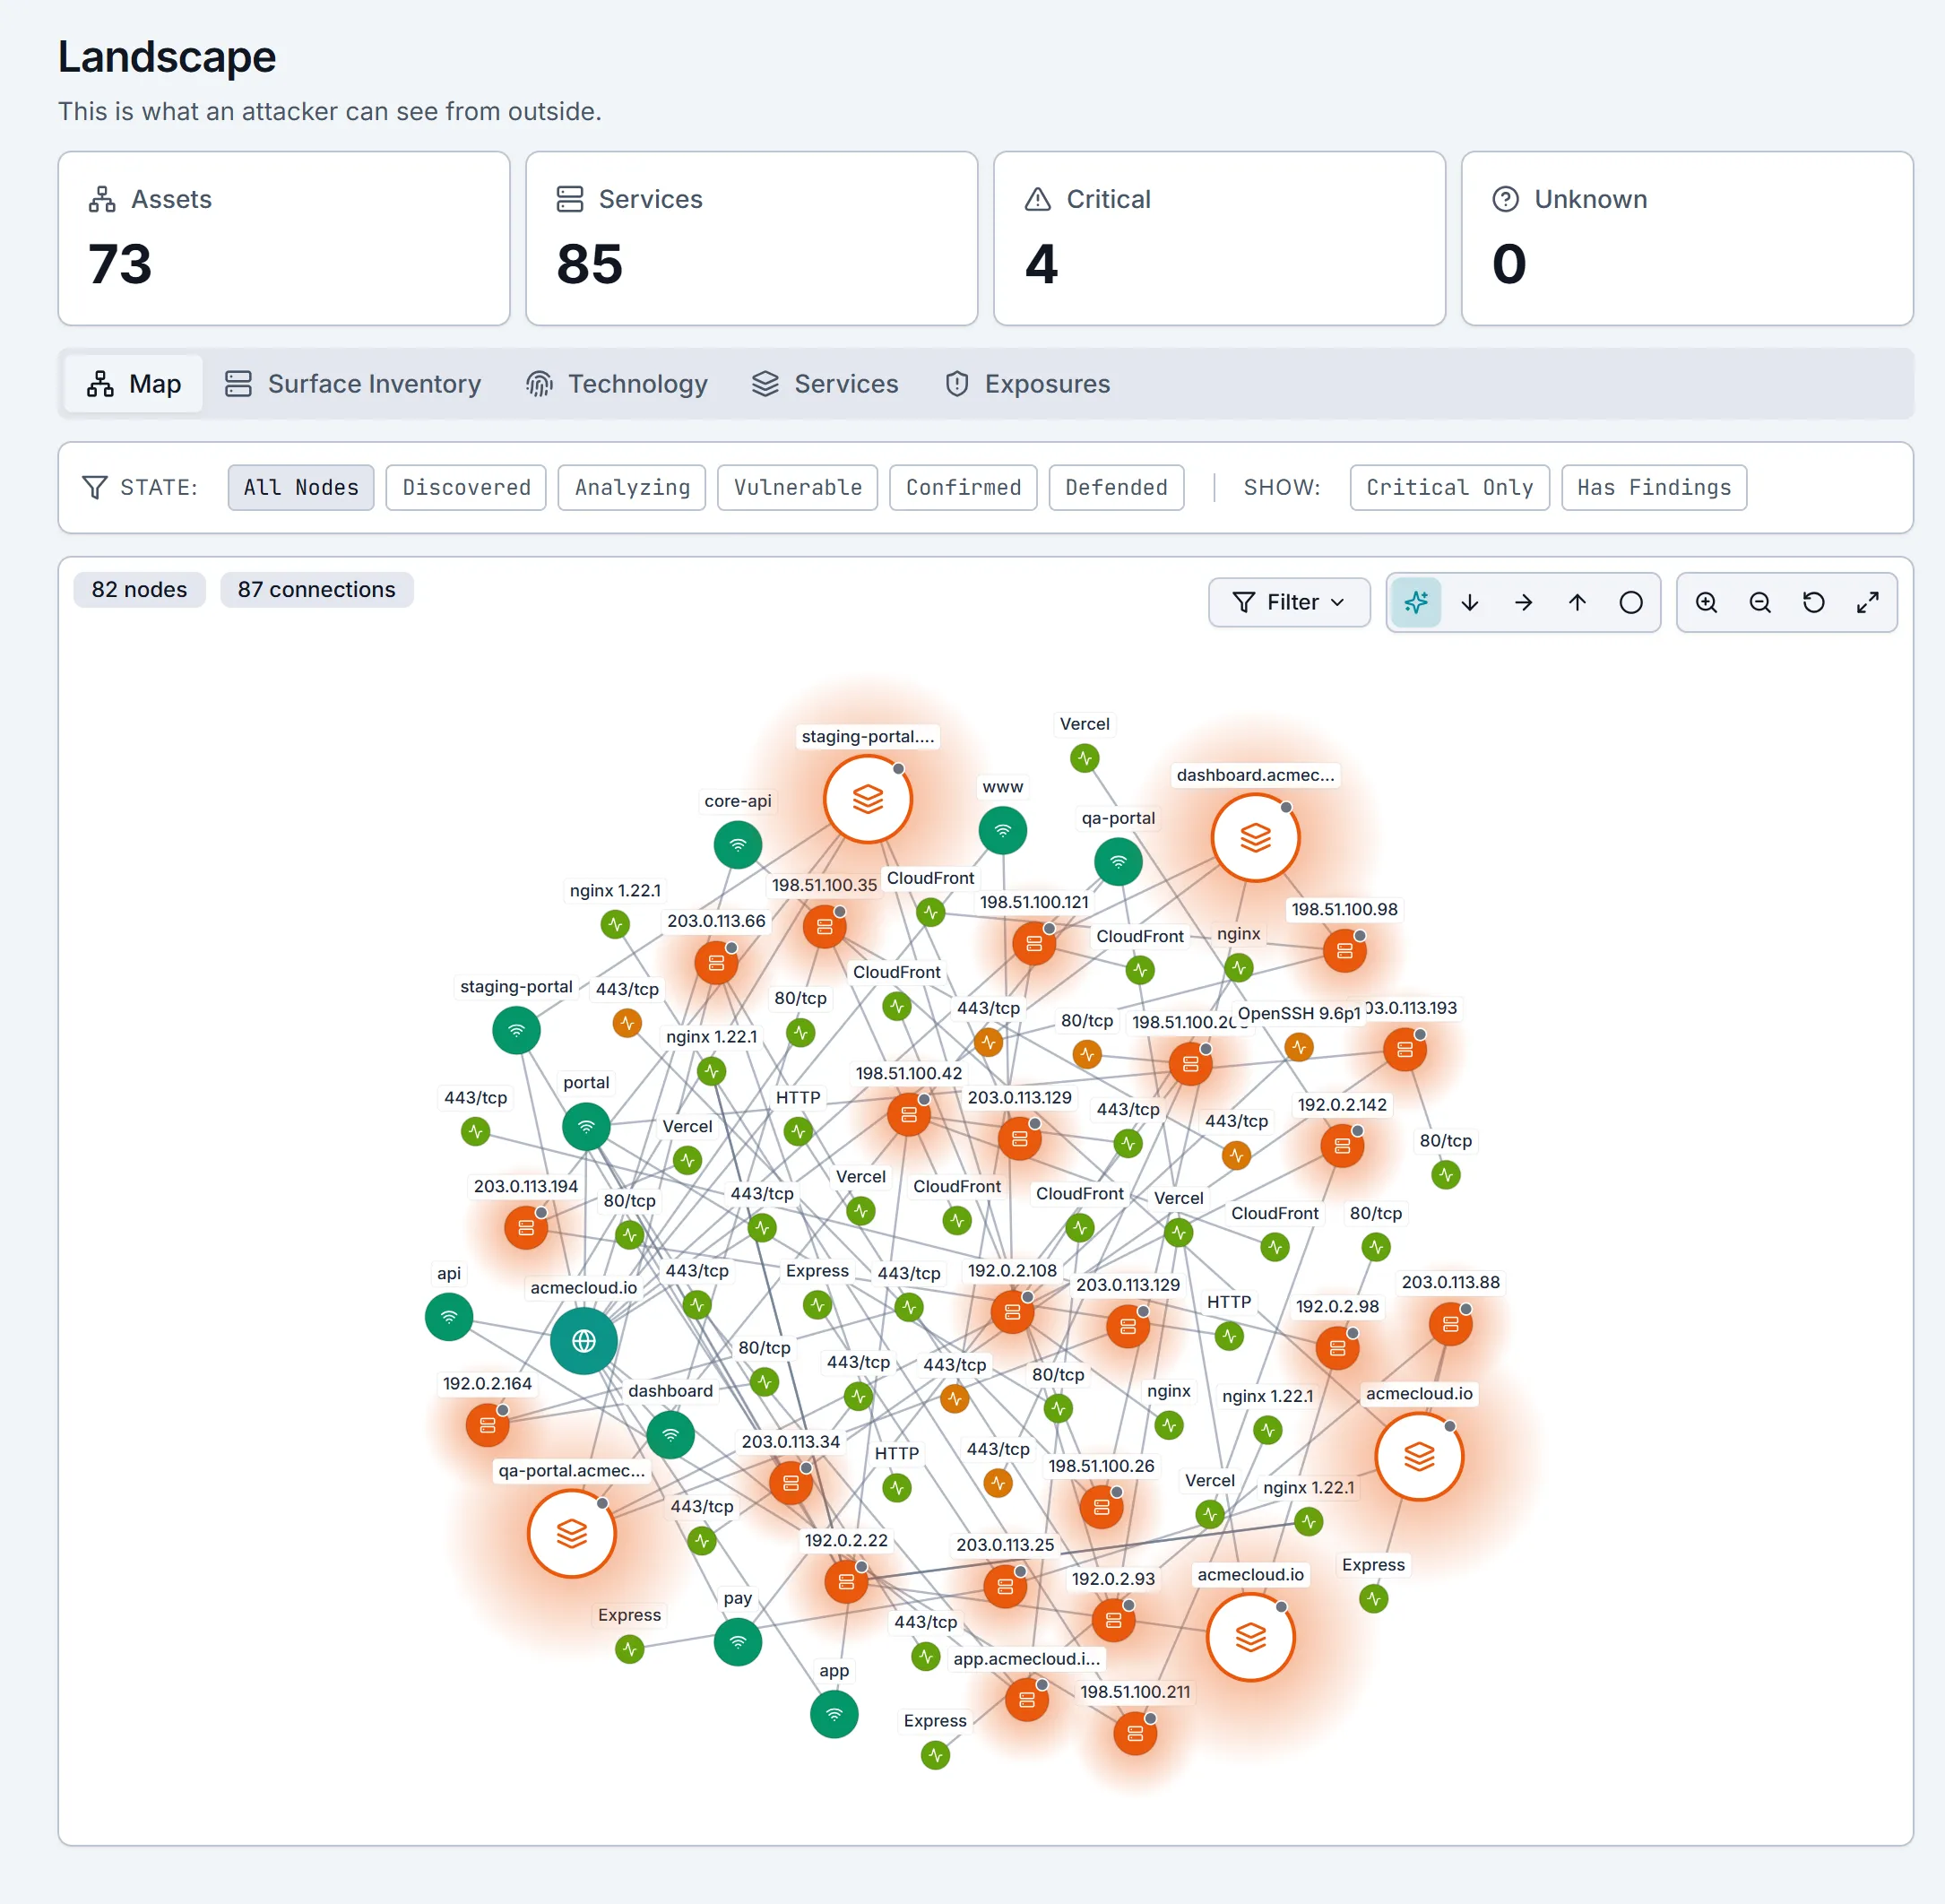
Discover
Map every endpoint before attackers find them
See your attack surface the way an attacker would: every asset, service, and port EdgeBreach found, and which ones it has analyzed, found vulnerable, or proven exploitable. Landscape scans are unlimited on every plan.
Key differentiators
What makes EdgeBreach different?
01
Discovery, chaining, and exploitation in one platform
Most tools in this space either simulate attacks (breach and attack simulation) or run automated scans, but rarely both. EdgeBreach discovers, chains, and exploits with evidence, unifying what competing tools sell separately.
02
Attack chain discovery
Real breaches aren't single vulnerabilities. They're chains. EdgeBreach automatically discovers how low-severity findings combine into critical exploits.
03
WAF bypass library
When a WAF blocks an attack, we don't stop. EdgeBreach tries 50+ bypass techniques to find what actually gets through, because attackers don't stop either.
04
Instant remediation validation
Fixed an issue? Click "Validate" and know immediately if it worked. No scheduling rescans. No waiting weeks. No hoping.
05
Evidence, not theories
Every proven finding includes screenshots, HTTP captures, and step-by-step reproduction. Evidence your security team can act on and your auditor can review.
06
Tests as often as you ship
EdgeBreach tests on your release schedule, so what you shipped since the last test gets tested, not just the version that existed on pentest day.
Safe by design
Proving exploitability without breaking things
EdgeBreach proves exploitability with bounded, non-destructive evidence, and enforces that before any action reaches your application. By default it does not delete, overwrite, or encrypt data; create backdoors, users, or keys; weaken configuration; change live business objects like orders, payments, or accounts; or run denial-of-service.
PROVED SAFELYThe proof is safe to run
EdgeBreach runs a read-only check or a controlled canary value and captures the evidence.
BLOCKEDThe next step would change your system
EdgeBreach doesn't send it. Unsafe actions are stopped before they reach your application.
REPORTEDOnly an unsafe path remains
The report records the verified prerequisite, the likely impact, and the step that was intentionally blocked. The finding stays actionable.
See what EdgeBreach proves in your application
We'll walk you through real findings, the evidence behind them, and the report you'd hand an auditor.
Book a demo