Continuous penetration testing
Your attack surface changes daily. Your pentest was months ago.
EdgeBreach tests your applications as often as you ship and proves which vulnerabilities an attacker can actually exploit, with the evidence to show for it.
The problem
Annual testing can't keep pace with how often you ship
Shipping got faster. Testing didn't.
1. Code ships faster than ever.
AI-assisted development turned quarter-long features into sprint-long ones. High-performing teams deploy on demand, often several times a day.
2. Every deploy changes your attack surface.
New endpoints, new parameters, new permission checks. None of them existed when your last pentest ran.
3. Attackers sped up too.
CrowdStrike's 2026 Global Threat Report describes an 89% increase in attacks by AI-enabled adversaries.
An annual pentest examines one version of your application. Everything you ship after that goes untested until next year's pentest. A better pentest firm improves the snapshot. It can't change the calendar.
Sources: DORA, 2025 State of AI-assisted Software Development; CrowdStrike, 2026 Global Threat Report.
How it works
Continuous testing that proves what's exploitable
EdgeBreach runs on our own reasoning model, trained specifically for software vulnerabilities. It tests the way an attacker works, on your release schedule instead of the calendar's.
01
Discover
Maps your exposed applications, APIs, and endpoints, and notices when they change.
02
Reason
Our reasoning model fingerprints each application and plans attacks for what's actually there, not a fixed checklist. It chains low-severity issues into the attack paths a real adversary would use.
03
Prove
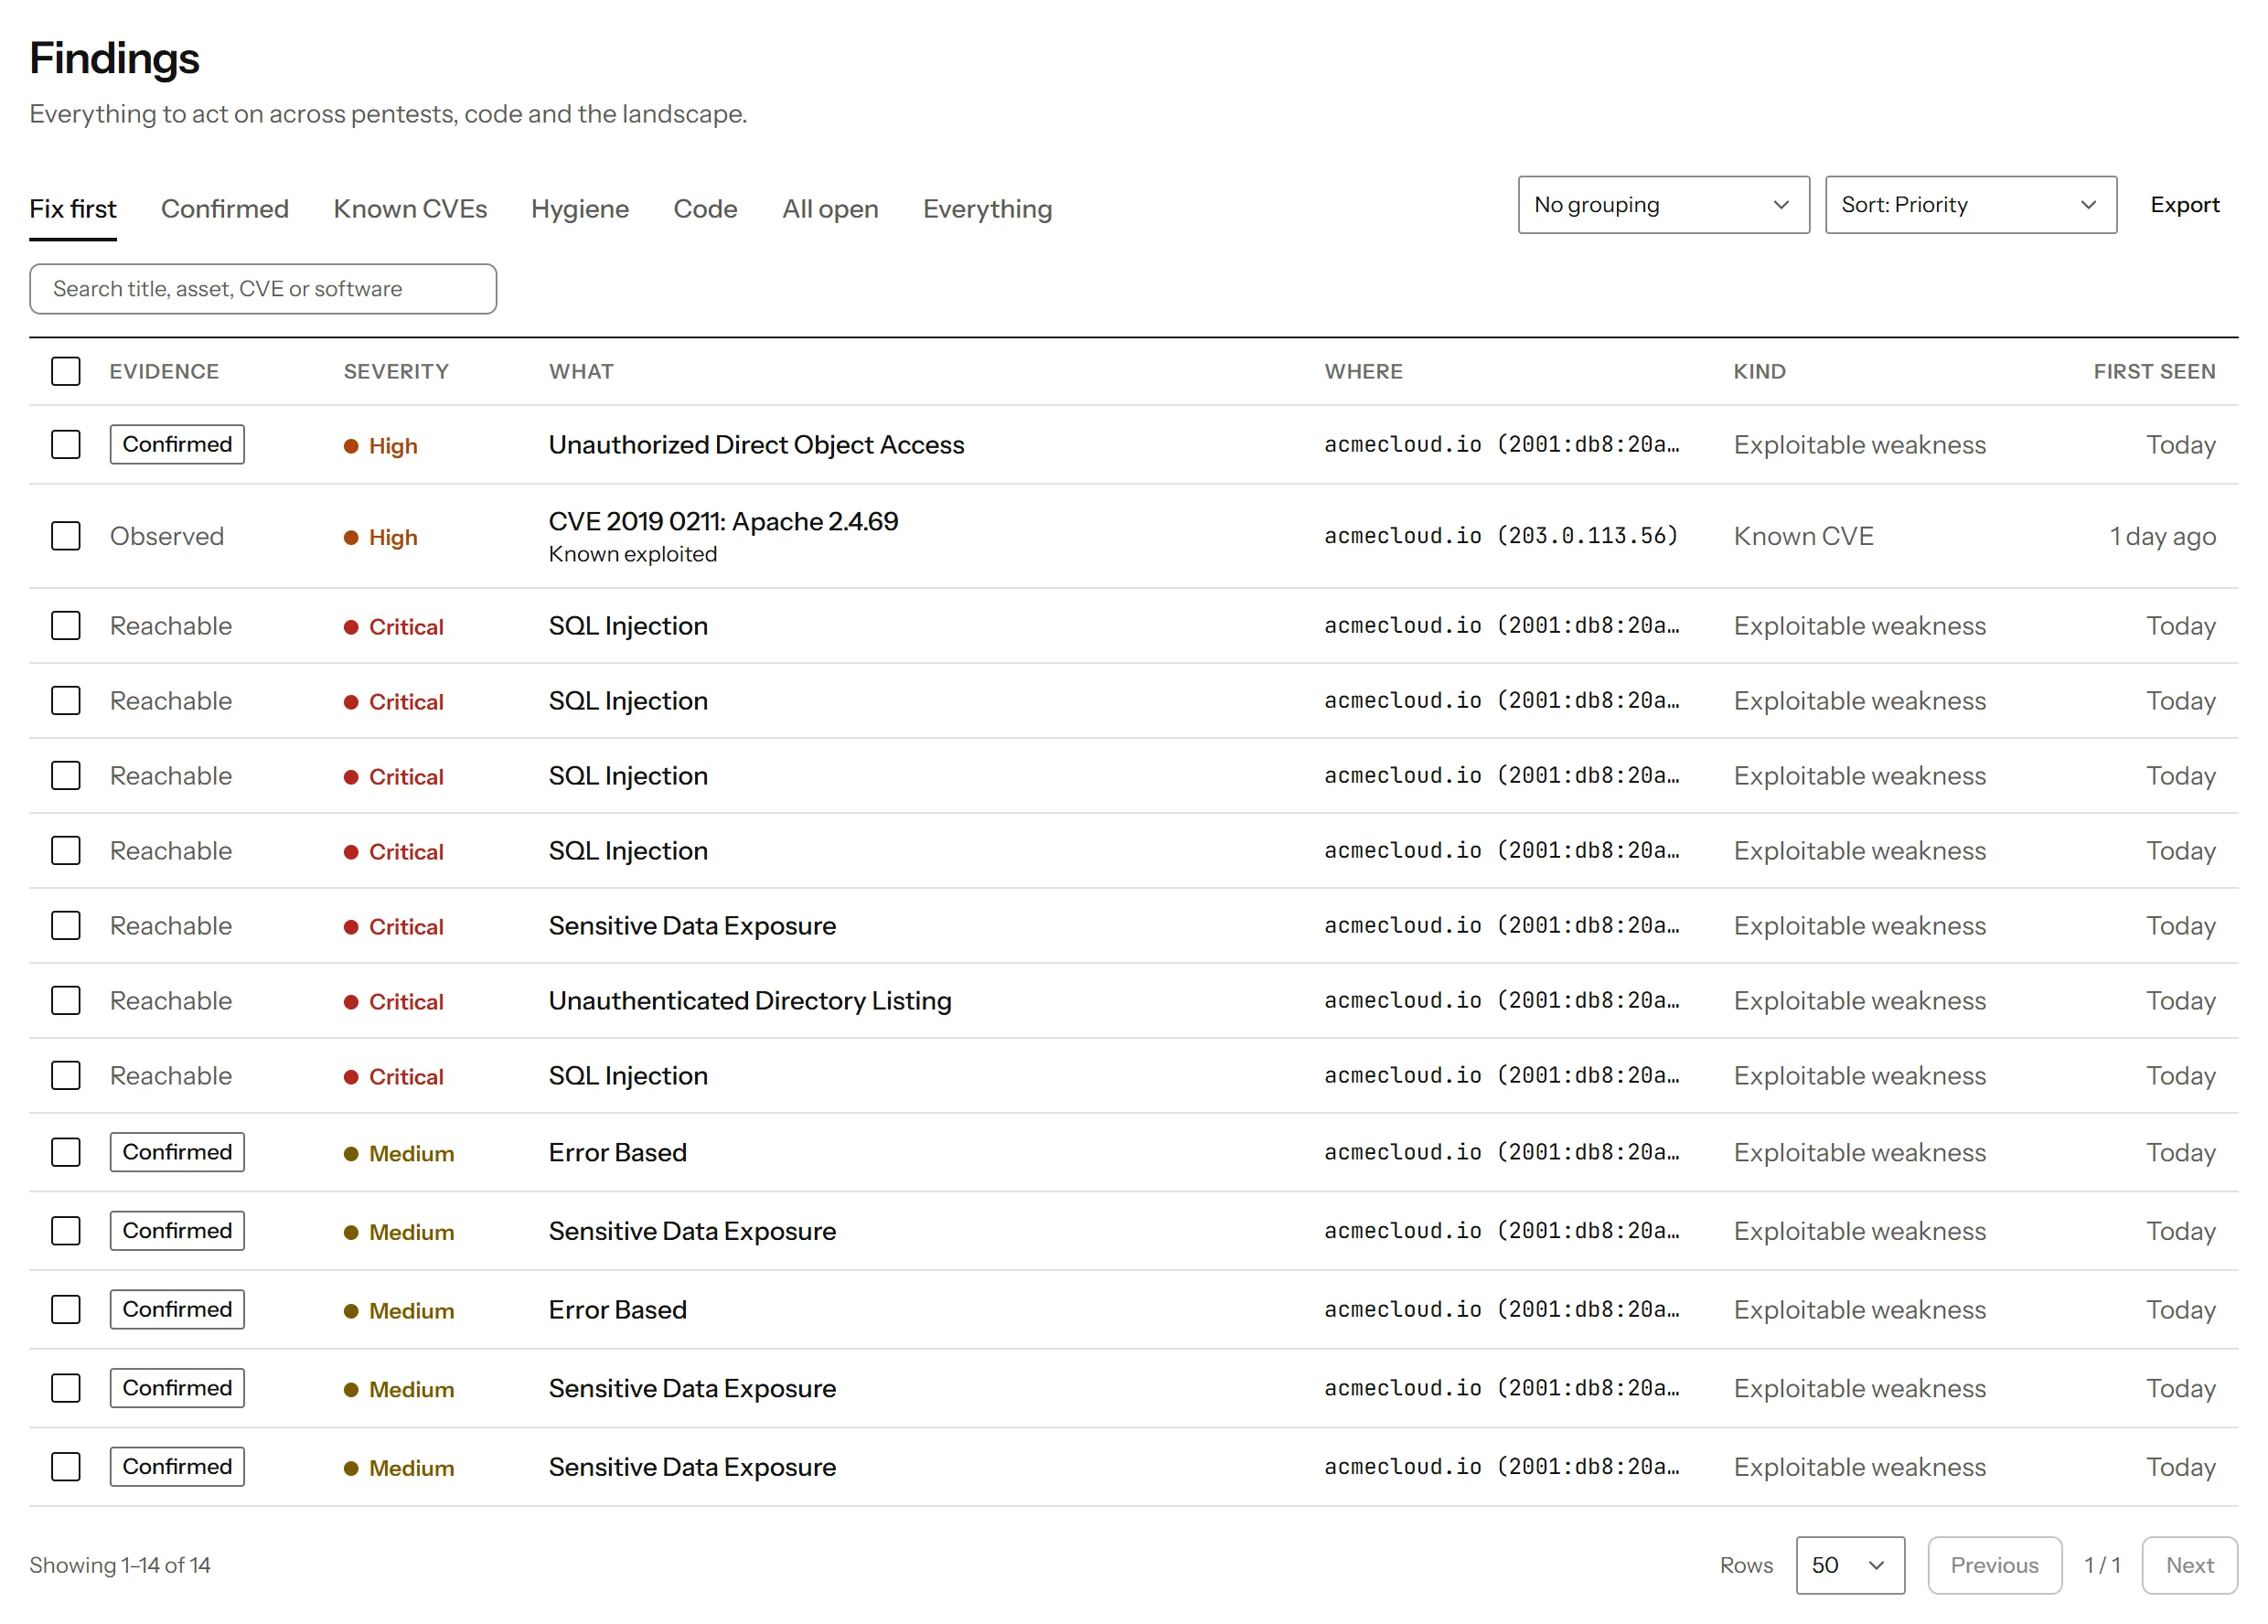
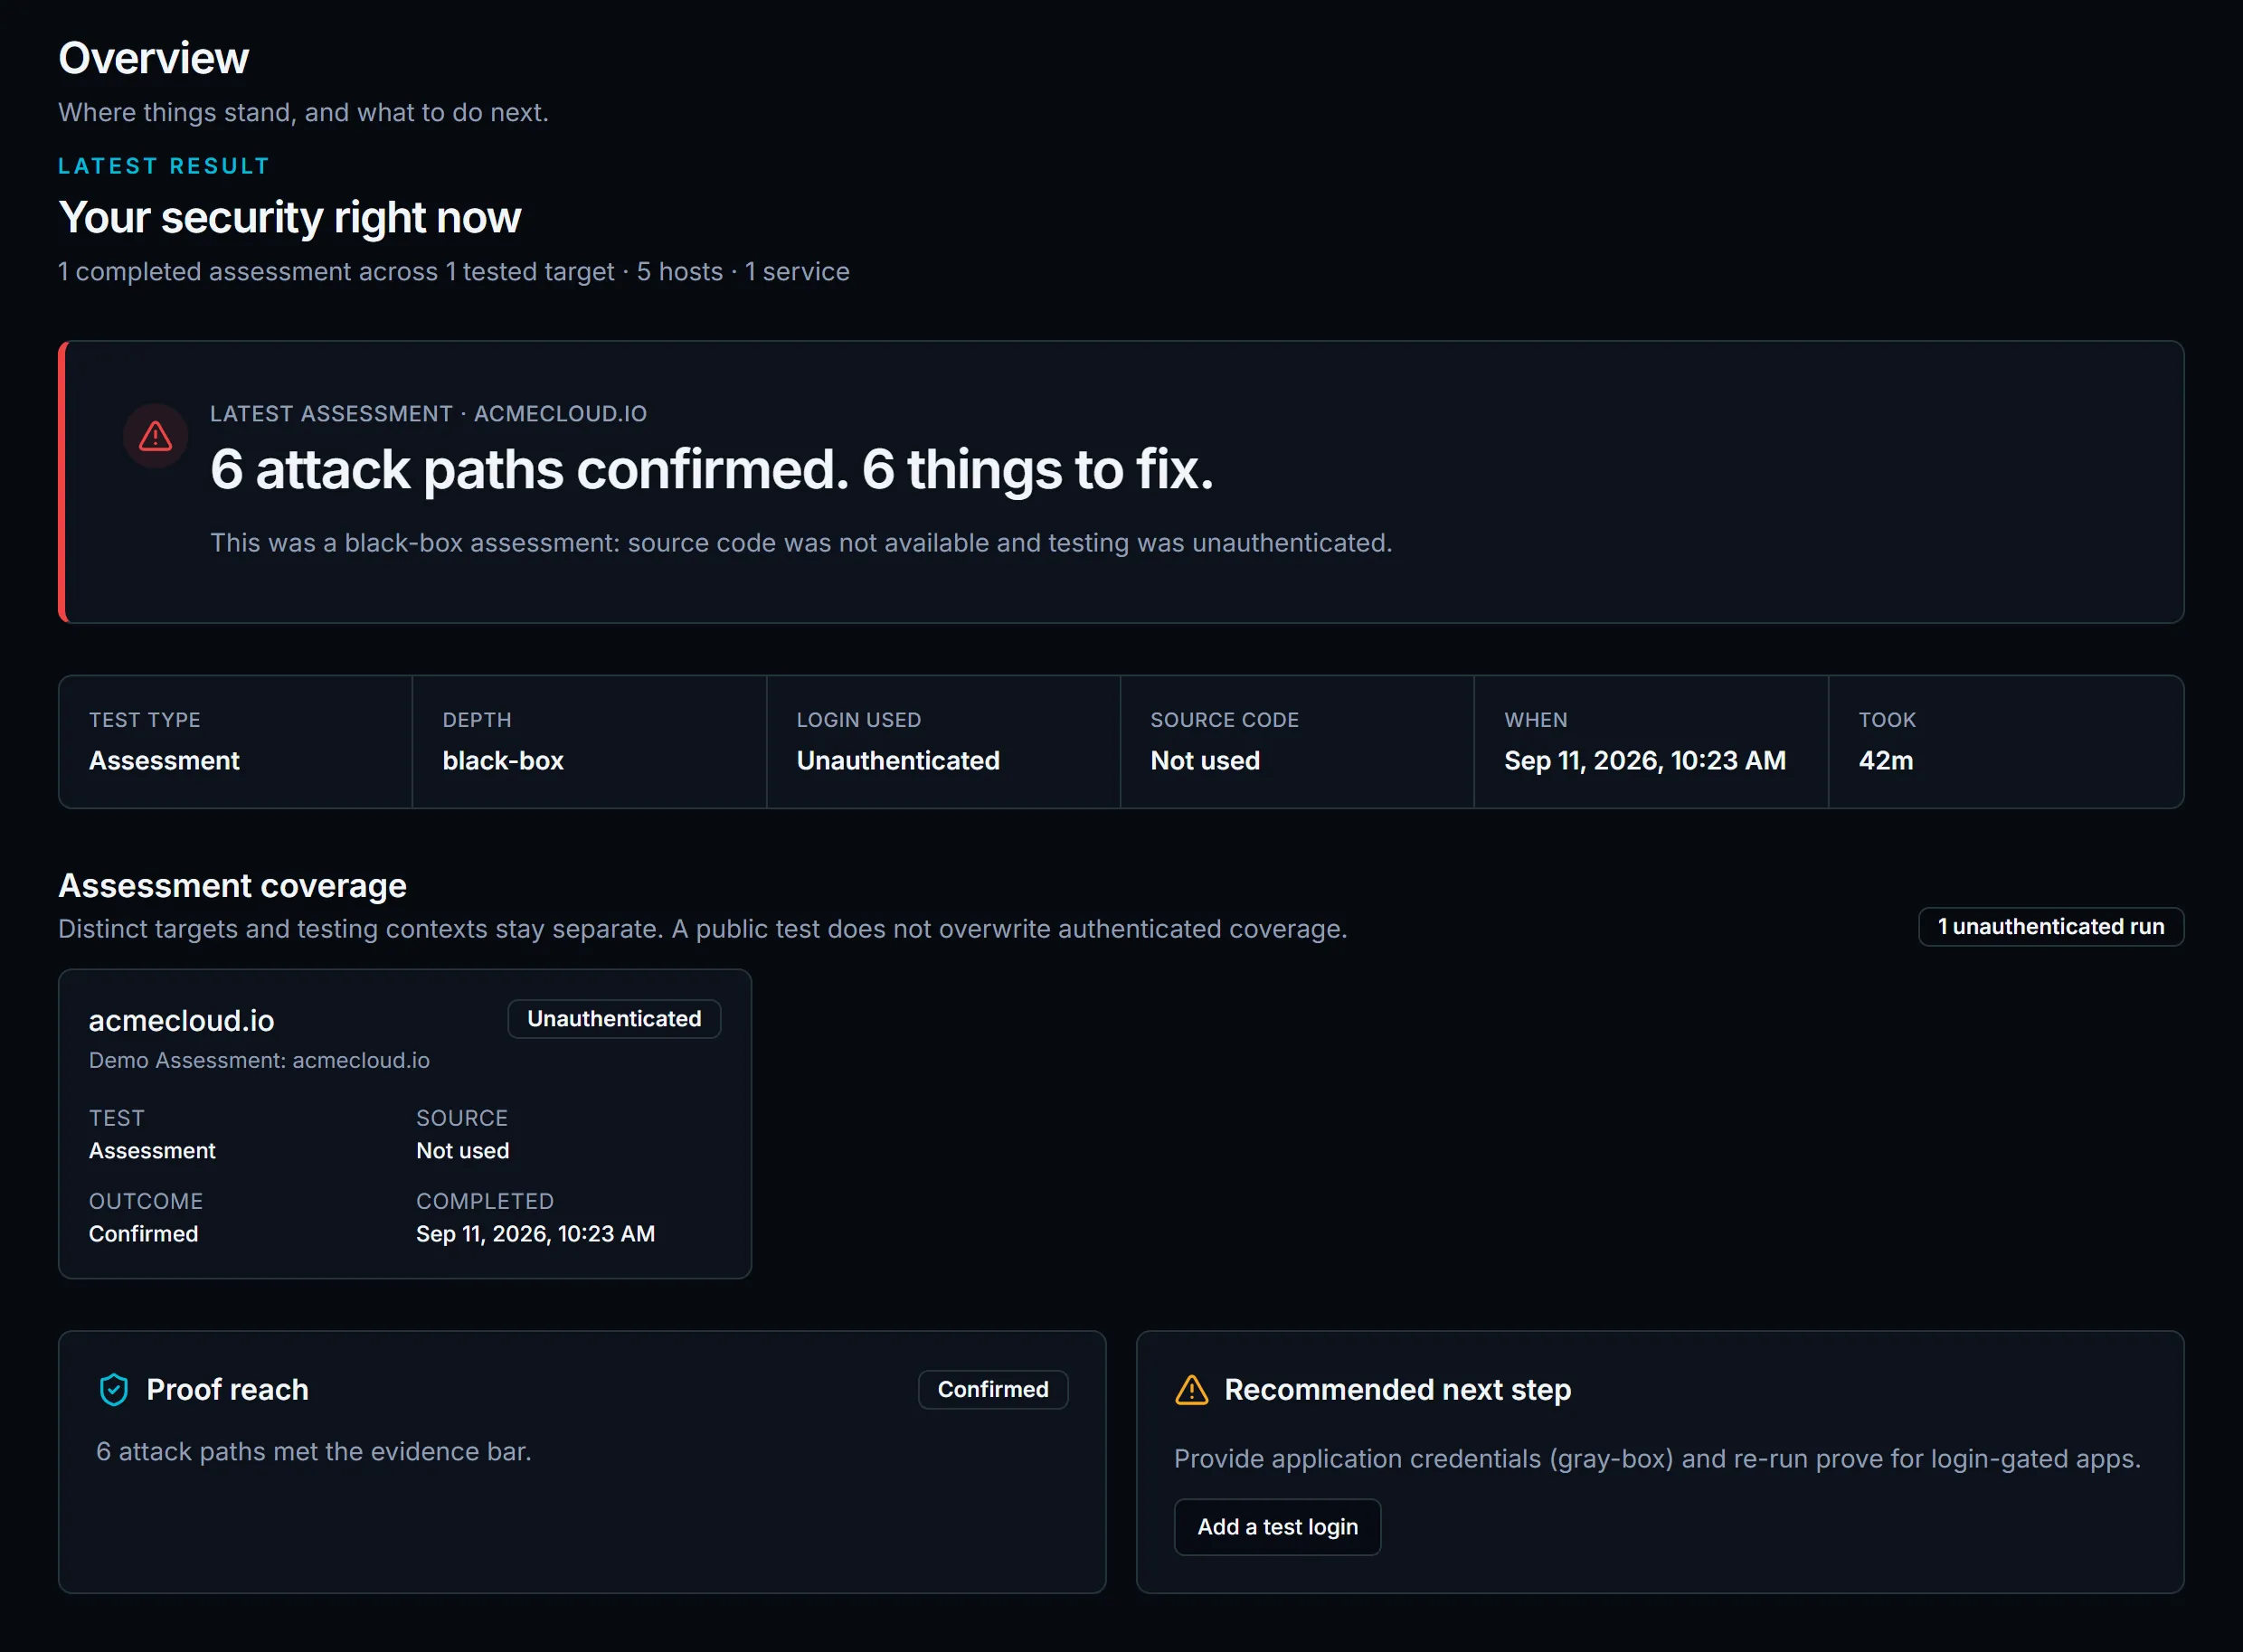
Attempts real exploitation, safely, and captures the evidence: the request and response, screenshots, and steps to reproduce. Findings it can't fully prove are reported with a confidence level, so you always know what you're looking at.
The difference
Testing more often only helps if you can trust the results
Running a scanner every day doesn't close the gap. It trades a coverage problem for a noise problem: long lists of possible issues that someone has to triage by hand. EdgeBreach shows its work instead.
Who it's for
Built for teams that ship software
Software companies
You deploy every week, or every day. EdgeBreach tests at that pace, so the code you shipped on Tuesday gets tested, not just the version that existed on pentest day.
Digital product agencies and dev shops
Tell prospects that the software you build for them is continuously penetration tested, and share the reports to back it up. It's a difference you can show, not just claim.
Agency partnershipsManaged service provider? Talk to us about partnering.
Compliance
Audit-ready reports, whenever you need them
EdgeBreach produces audit-ready reports for frameworks like SOC 2 and PCI-DSS. Run it alongside your annual pentest or rely on it on its own. That's your call, and we'll give you the framework mapping to take to your auditor.
Cost
- $299
- STARTING PRICE PER MONTH
- $15K to $150K+
- TYPICAL ANNUAL PENTEST ENGAGEMENT, MARKET RANGE
- Weekly to on-demand
- TESTING CADENCE, BY PLAN
Questions
Does EdgeBreach replace our annual pentest?
That depends on your auditor and the frameworks you report against. EdgeBreach produces audit-ready reports for frameworks like SOC 2 and PCI-DSS. You can use them on their own, or run EdgeBreach alongside an annual engagement to cover everything you ship in between. We'll give you the framework mapping to take to your auditor.
How is this different from a vulnerability scanner?
A scanner matches responses against known patterns and reports what might be vulnerable. EdgeBreach reasons about your specific application, attempts real exploitation, and shows you the evidence for what it proved. Anything it couldn't fully prove is labeled with a confidence level instead of being presented as fact.
What makes your AI different?
Many security tools bolt a general-purpose AI model onto an existing scanner. EdgeBreach's core engine is our own reasoning model, trained specifically for software vulnerabilities and built to drive the testing itself: deciding what to try, observing what happens, and adapting mid-test. That's what AI-native means to us.
Do you need our source code?
No. Black-box testing works from the outside, the way an attacker would. If you choose white-box testing, your source code is processed in memory only, never written to disk or stored, and never used to train our models.
Is it safe to run against production?
EdgeBreach throttles automatically, detects rate limiting, and backs off at signs of system stress. You can set scan intensity and timing windows.
Who is EdgeBreach for?
Companies that build and ship their own software, and the agencies and dev shops that build software for clients. Plans start at $299/month.
How much have you shipped since your last pentest?
Find out what's exploitable in the version you're running today.
Book a demo